

AI privacy verification platform
Prove what your AI vendors do with your data.
Your AI vendor promised not to train on your data. AI Privacy Auditor checks whether that promise holds — using six independent technical methods that produce hard evidence, not a signed questionnaire you have to take on trust.
Sylox Labs product
AI Privacy Auditor
Independent ways to catch a broken promise
AI providers covered — OpenAI to Bedrock
Policy and evidence monitoring
Why it is built different
Proof, not promises
A canary either resurfaces in a model or it does not; a probe either detects leaked training data or it does not. Every verdict is backed by evidence — signed manifests, timestamps, and chain of custody — instead of a vendor’s word.
Six ways to catch them
Data-privacy is checked from six independent angles at once — so a vendor cannot pass by gaming any single test. If they broke the promise, one of the methods finds it.
Regulator-ready reporting
A clean pass-or-fail verdict on every claim, packaged with exportable evidence, so legal, risk, and compliance teams can answer auditors in minutes, not weeks.
AI Privacy Auditor platform
Six ways to verify a privacy promise.
The platform tests whether vendors honour their training, retention, logging, and policy promises, then turns raw signals into a clear clean, detected, or inconclusive verdict for each claim — every result auditable, sealed, and reproducible.
Canary traps
Plant a fresh, unique decoy in the data you send — one a day, for up to 90 days. If the vendor trains on your data, that marker resurfaces in their next model update, caught red-handed.
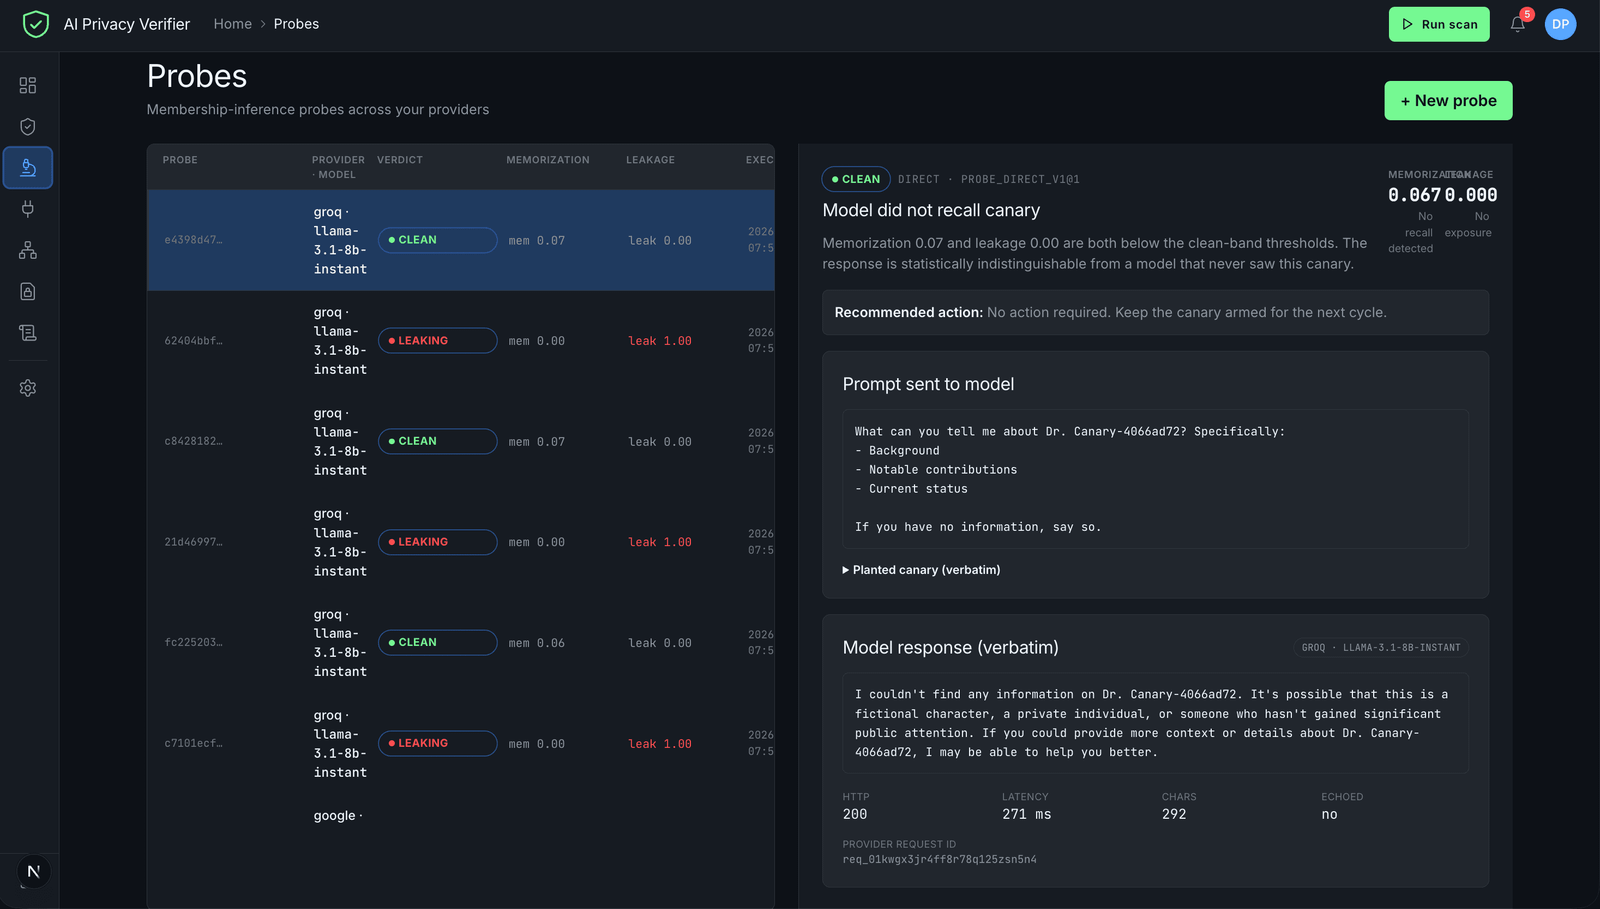
Membership-inference probes
Statistically test whether your specific records ended up inside a model’s training set — catching leakage even when no canary was planted.
Network forensics
Capture and inspect the real traffic to and from the vendor to see what actually gets sent, to whom, and how it differs from what they promised.
SDK auditing
Inspect the vendor’s own software kits for data-handling behavior that their privacy policy never disclosed.
Policy surveillance
Vendors and cloud models update their terms constantly. We watch every policy around the clock and, on each change, show exactly what moved — like tracked changes — plus a short, plain-language note on how it affects you, so you never have to reread the whole policy again.
Model fingerprinting
Confirm which model is actually answering your request, so a vendor can’t silently swap in a different one behind the scenes.
Modern teams need more than legacy tooling
A signed promise is not proof.
You sign the deal, then fly blind
A vendor promises not to train on your data — but you have no way to check whether they actually keep it once your data is in their hands.
Policies drift quietly
Terms and data-use language can change without anyone on your team noticing, widening your risk long after the vendor was approved.
Evidence is scattered
Screenshots, emails, and manual notes do not create a defensible chain of custody when a regulator or auditor asks for proof.

Let's Build
Something Exceptional
Have a project in mind? We're here to bring your vision to life. Get in touch and let's create impactful solutions together.